A2A and MCP: The Open Protocol Stack Powering theMulti-Agent SOC
An alert fires at 2am. A Triage Agent inside Splunk enriches it in seconds. Then the workflow stops. Someone has to open a second tool to trigger the response. Someone…
An alert fires at 2am. A Triage Agent inside Splunk enriches it in seconds. Then the workflow stops. Someone has to open a second tool to trigger the response. Someone…
For the latest discoveries in cyber research for the week of 24th August, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Latvia’s Road Traffic Safety Directorate (CSDD) has confirmed…
This release has something for everyone: scanner modules, payloads, and exploits. This release’s scanners cover Drupal, PanOS, WordPress, and SCADA; this release’s exploits cover Tenable, Flowise, CheckPoint, Langflow, Ruby, and…
Welcome to this week’s edition of the Threat Source newsletter. Hello, everyone. Long time reader, first time writer here at the Threat Source newsletter! I wanted to start out by…
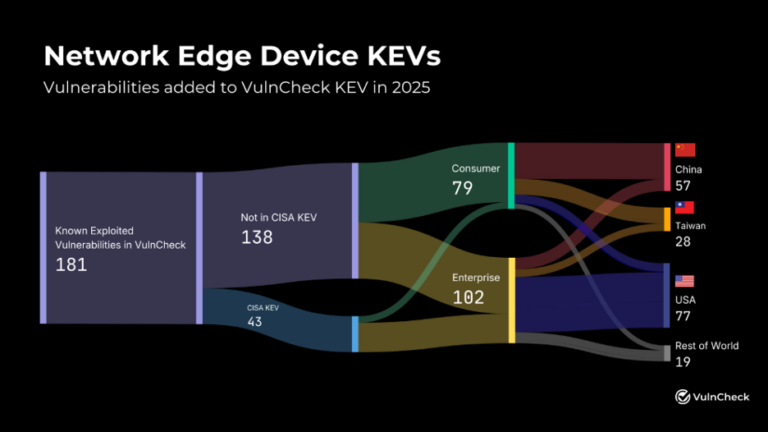
Network edge vulnerabilities are accelerating. Cato’s cloud-native architecture reduces customers’ attack surface and shortens exposure to emerging vulnerabilities. The Cato CVE Exposure Calculator shows what that difference could mean for…
CVE-2026-19490: Critical Citrix NetScaler Authentication Bypass Exposes Enterprise Gateways Cloud Software Group has released critical security updates to address CVE-2026-19490, an authentication bypass vulnerability (CWE-288) in NetScaler ADC and NetScaler…
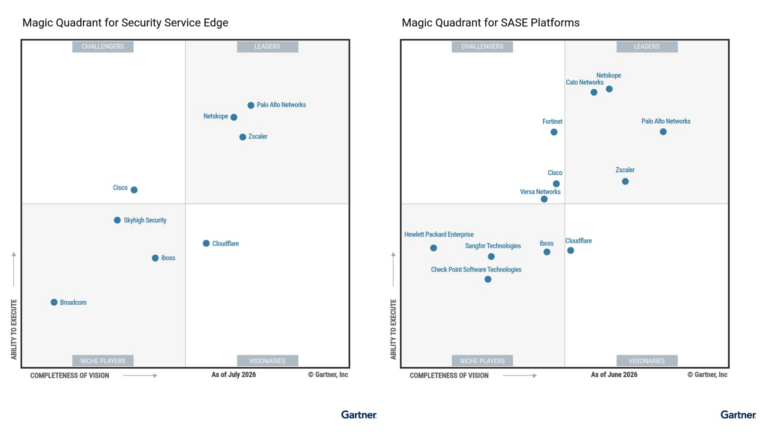
As organizations race to deploy agentic AI, legacy network security solutions are ill-equipped to keep up, forcing productivity tradeoffs while exposing coverage gaps. At the same time, Frontier AI is…
A joint cybersecurity advisory released by multiple U.S. government agencies warns that threat actors are using AI-generated exploitation scripts to target exposed Siemens S7 Series PLCs across critical infrastructure sectors….
The alert problem every SOC knows Security operations centers are drowning in alerts. Volume grows faster than teams can hire; many of those alerts turn out to be false positives,…
Research by: Jiří Vinopal (@vinopaljiri) Abstract What if a trusted security component could be repurposed into an attacker-controlled kernel primitive? What if a signed Microsoft remediation driver could be instructed…