How your guardrails might become the attacker’s best friend
Welcome to this week’s edition of the Threat Source newsletter. Hello, everyone. Long time reader, first time writer here at

Welcome to this week’s edition of the Threat Source newsletter. Hello, everyone. Long time reader, first time writer here at
AI agents comprise models, instructions, data, and tools, so thoroughly investigating potential security risks requires evidence from several components. As
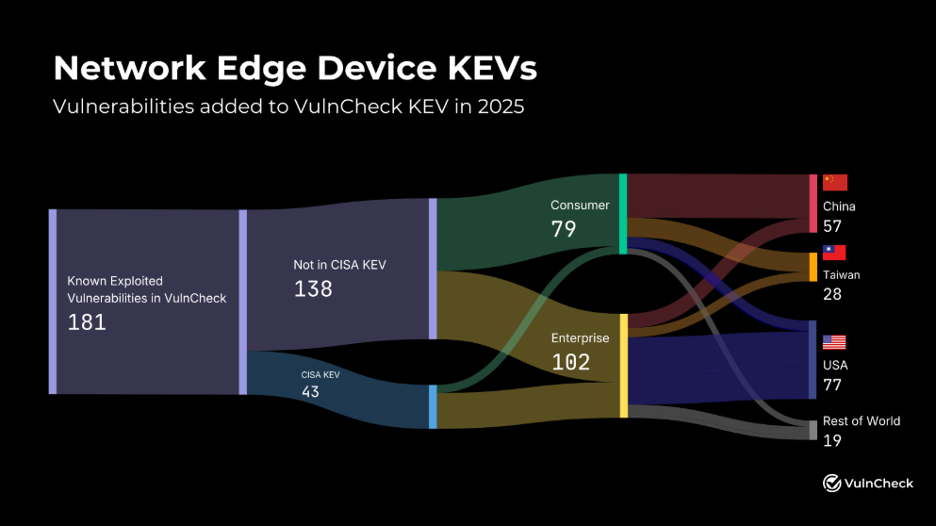
Network edge vulnerabilities are accelerating. Cato’s cloud-native architecture reduces customers’ attack surface and shortens exposure to emerging vulnerabilities. The Cato
Building a multi-region active-active architecture with Amazon CloudFront requires careful coordination of traffic routing to address performance, traffic management, and
This is Part 1 of a three-part series. Read Part 2 and Part 3. Table of Contents Introduction Motivating Example:
CVE-2026-19490: Critical Citrix NetScaler Authentication Bypass Exposes Enterprise Gateways Cloud Software Group has released critical security updates to address CVE-2026-19490,
“This expansion enables customers to easily manage complex, high-density AI clusters alongside non-AI workloads. Customers will also now be able
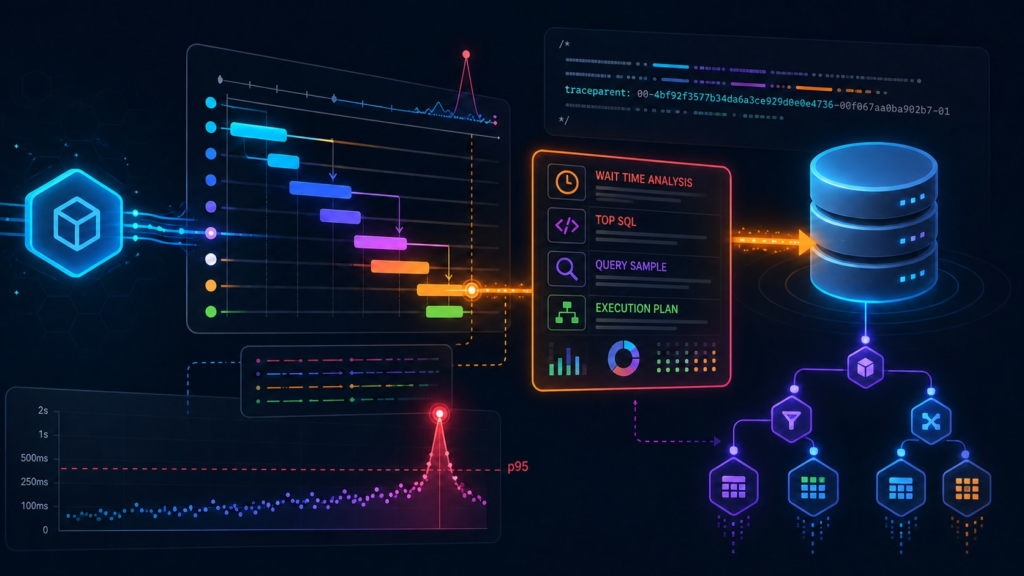
The alert fires on p95 latency. A high-traffic API endpoint whose p95 normally sits under 100ms is now sitting at
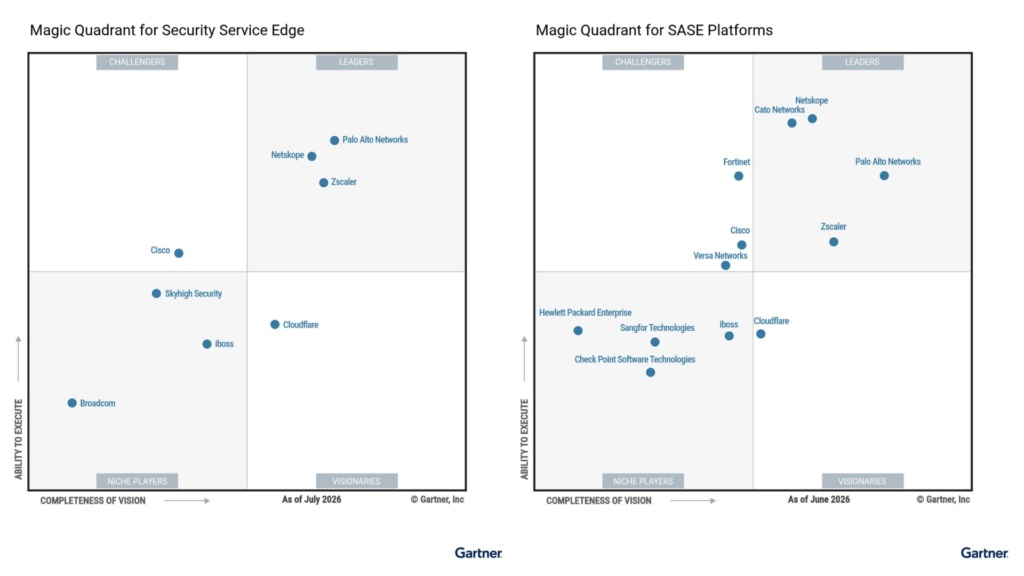
As organizations race to deploy agentic AI, legacy network security solutions are ill-equipped to keep up, forcing productivity tradeoffs while
CloudFront Functions (CF2) lets you run lightweight code inside Amazon CloudFront Points-of-Presences (POPs) to analyze and manipulate viewer requests and